SME Cybersecurity: What Keele’s Award-Winning Training Partnership Offers UK Small Businesses




SME Cybersecurity News – Helping Keep UK SMEs CYBERSafe with Daily News, Threat Intel & Best-Practice
SECURUS Communications Ltd
Securus is a managed communications Operator, providing next-generation network infrastructure and value added services to Managed Hosting providers and the ‘cloud generation’ of enterprises. Securus priority is to offer communication services that represent excellent value for money and are backed by exceptional levels of support.
Contact Securus
Securus Communications Ltd
Station Road, Landmark house, Hook, England RG27 9HA, GB
T: Enquiries: 03451 283457 | Service Desk: 03451 283458
Securus on LinkedIn | Securus on “X” | https://securuscomms.com
Gibraltar: Friday, 23 October 2026 – 07:00 CET
SME Cybersecurity: What Keele’s Award-Winning Training Partnership Offers UK Small Businesses
By: Iain Fraser – Cybersecurity Journalist
Published in Collaboration with:
Securus Communications Ltd
SMECyberInsights.co.uk – First for SME Cybersecurity
Google Indexed on: CET | SERPS: LLM(AI) Google
#CyberJourno #CyberEssentials #CyberResilience #CyberSafe #CyberSecurity #Cybersecurity #NCSC #SME #SMECyberInsights #SMECybersecurity #SMECyberInsights #ThreatIntelligence #Securus #CyberTraining
SME Cybersecurity: What Keele’s Award-Winning Training Partnership Offers UK Small Businesses
A Keele Business School partnership has received international recognition for helping smaller organisations improve Cybersecurity. Reported results include increased multi-factor authentication adoption and stronger incident reporting. For UK SMEs, the useful lesson is that training should lead to implemented controls and measurable changes, not simply attendance certificates. However, reported outcomes need careful interpretation.
SME Cybersecurity: What the Keele partnership achieved
Cybersecurity training earns its place in an SME budget when it changes how the business operates. Keele Business School’s award-winning partnership offers an example of training linked to practical improvements rather than awareness alone.
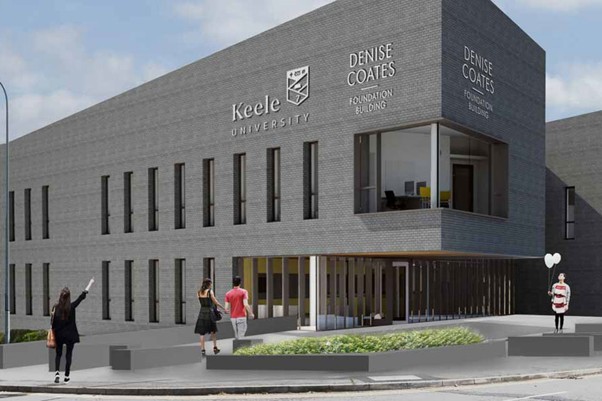
According to Keele University’s announcement, published on 16 October 2026, the Staffordshire Cyber Resilience Programme received a Gold EFMD Excellence in Practice Award. Keele reports that it was one of four business schools worldwide to receive Gold recognition in 2026. The programme brought together Keele Business School, IT support company Hixon Group and Staffordshire Chamber of Commerce. Its significance for SMEs lies less in the trophy than in its delivery model: academic expertise, operational threat knowledge and local business access working together.
Why was the programme developed?
The programme responded to an identified gap between local threats and smaller firms’ ability to manage them. Keele reports that Hixon Group detected increased successful ransomware deployments against local micro-businesses in 2024. Ransomware is malicious software used to deny access to systems or data, often alongside demands for payment. For a micro-business, losing access to bookings, customer records or accounts can interrupt trading. The partners identified limited access to coordinated, affordable Cybersecurity support. That is a recognisable SME problem. Owners may have outsourced IT but little clarity about security responsibilities, while staff face suspicious emails without knowing whom to contact. The partnership connected those needs with practical support. However, its success should not be interpreted as proof that any training course will deliver equivalent results. Content, implementation support and follow-through matter.
What do the reported results actually show?
Keele reports that the programme reached 2,000 individuals in its first quarter. It also reports a 73% increase in multi-factor authentication usage among participants, alongside a reduction of nearly 60% in reported cyber risk incidents. Multi-factor authentication, or MFA, requires more than one form of evidence when someone signs in.
It helps prevent a stolen password from being sufficient to access an account. The announcement also states that every participating organisation reported implementing at least three additional security controls. These findings suggest that learning translated into action.
However, the announcement does not provide the detailed evaluation methodology, participant baseline or a comparison group. The 73% figure should not be presented as a percentage-point increase or a final adoption rate. Similarly, the estimated £300,000 in avoided potential losses is an economic model, not verified cash savings. The findings are encouraging, but they do not establish a guaranteed return for another SME.
How UK SMEs can turn training into stronger resilience
Effective training should produce specific changes in controls, responsibilities and reporting behaviour. That principle is useful even for firms unable to join a university-led programme. The NCSC’s Small organisations guide to Cybersecurity provides a starting point covering backups, devices, accounts and scams. It also emphasises shared responsibility rather than leaving protection with one person.
Start with three business-specific outcomes
Choose a short list of improvements before commissioning training. For example:
* Enable MFA on every supported business email account.
* Introduce independent verification for supplier bank-detail changes.
* Establish a reporting route that every employee can use. Each outcome needs an owner and completion date. An outsourced IT provider might configure authentication, while finance owns payment verification and a director sponsors reporting. This avoids a common failure: employees understand the risks, but nobody has authority to change the systems or processes behind them.
Make reporting safe, fast and useful
Keele reports increased voluntary reporting of near misses, suggesting that participants became more comfortable raising concerns. A near miss is an event that could have caused harm but was interrupted or avoided.
For SMEs, that matters because delayed reporting can give an attacker more time. Staff should know that promptly reporting an accidental click is helpful, not an invitation to blame.
Provide a named contact and a backup route if email is unavailable. Acknowledge reports, explain what happens next and share anonymised lessons. More reports may initially indicate stronger awareness rather than deteriorating security.
Connect learning to technical controls
Training cannot compensate for insecure systems. Pair staff guidance with checks against Cyber Essentials, the government-recommended baseline covering five technical control areas. Ask your provider to demonstrate implemented changes rather than confirm that training happened. Useful evidence includes MFA coverage, removal of unnecessary administrator privileges and completion of security updates. Measure progress through implemented controls and tested processes. Completion rates are useful administrative information, but they are not evidence that the business can detect, contain or recover from an incident.
FAQs
Is Cybersecurity training worthwhile for a very small business?
Yes, when it addresses the business’s actual risks and leads to practical changes. A short session covering suspicious messages, payment verification and reporting can be useful. However, training should complement secure accounts, updated devices and tested backups, rather than substitute for technical protection or clear management responsibility.
How can an SME improve security without employing a specialist?
Start with free NCSC guidance, assign a director to oversee priorities and agree specific tasks with your IT provider. Focus on MFA, updates, access permissions and backups. Local business networks or university partnerships may offer additional support, but check eligibility, scope and costs before relying on availability.
How should a business measure whether training is working?
Measure changes in behaviour and implemented safeguards, not attendance alone. Check whether staff report suspicious activity promptly, finance verifies bank-detail changes and supported accounts have MFA enabled. Review near misses constructively. Increased reporting can be a positive sign, particularly where employees previously stayed silent through uncertainty or embarrassment.
FAQ note: These FAQs are based on recurring live audience questions and discussion themes from Reddit and Quora, helping ensure each article answers what SME readers are actively asking in the real world.
Conclusion
Keele’s partnership illustrates the value of connecting practical expertise, accessible support and measurable action. The award is recognition, not a guarantee of protection. For your next training review, select three security improvements, assign owners and check that each change is working within 30 days.
What is a VPN & Does my SME Need one? A VPN is a Virtual Private Network a method of securing your communications credentials. When it comes to SMEs, the choice of VPNs can significantly impact the security and efficiency of their operations. NordVPN secures your Internet data with military-grade encryption, ensures your activity remains private and helps bypass geographic content restrictions online. Join NordVPN Today and Save up to 73% and Get 3 months Extra Free – Rude Not to …!
SMECYBER Insights – Helping Keep Small Business CYBERSafe!
Launched in 2020 by Cybersecurity Journalist Iain Fraser and his team at IfOnly… SMECYBERInsights was developed to be the go-to platform providing definitive, reliable & actionable Cybersecurity News, Intel, Awareness & Training specifically written and curated for Small Business & Enterprise Owners, Partners and Directors throughout the UK. #SMECyberInsights #SMECyberSecurity #CyberAttack #CyberAwareness #Compliance #DDoS #Fraud #Ransomware #ScamAlert #SME #SmallBusiness #SmallBusinessOwner #ThreatIntel